
Privacy & PII
userGist ships with a default-deny posture for sensitive properties. This page covers the allow-list, deletion, and the DPA.
PII allow-list
By default, UserGist removes matching sensitive properties before storage. The default filter covers exact or namespaced contact and identity keys, including:
email, email_address, phone, phone_number, mobile, ssn, tax_id,
national_id, passport, common name fields, postal addresses, and birth dates.
If your business legitimately needs one (e.g. email for list exports), open App settings → Privacy and add it to the allow-list.
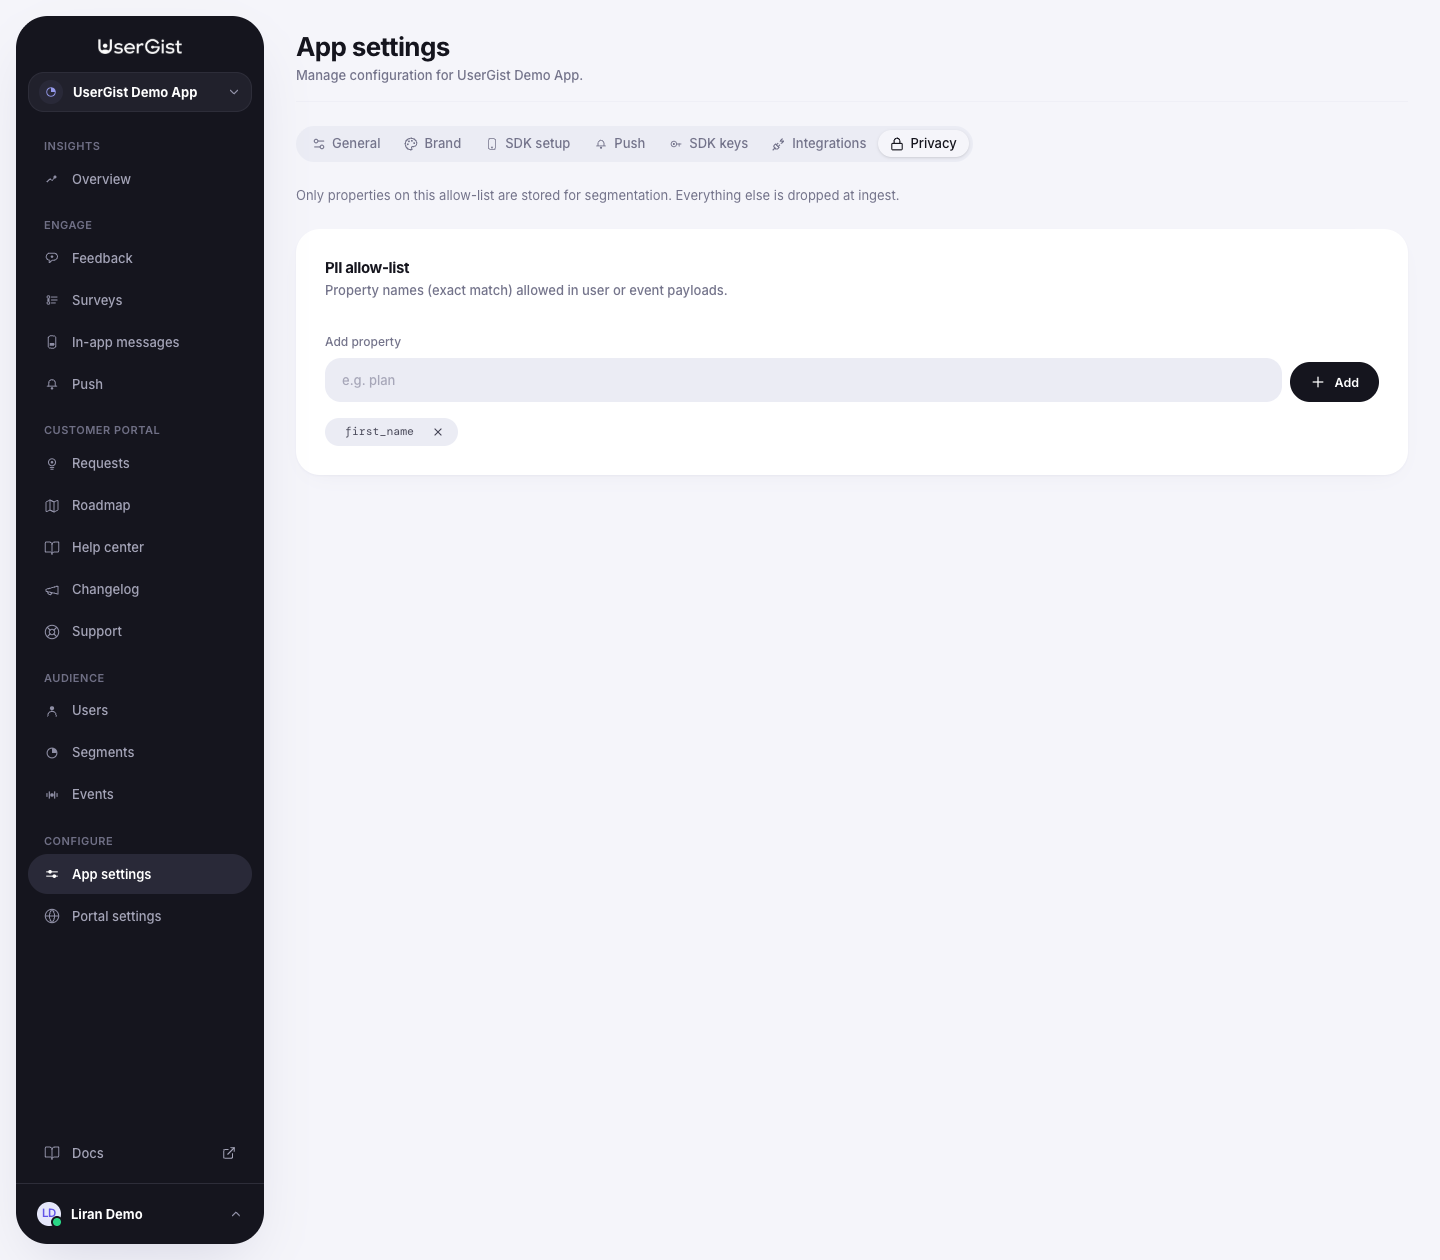
The filter accepts the event or identify call and drops only matching properties
that are not on the allow-list. Allow-list entries match the complete property
key case-insensitively, including namespaced keys such as user.email.
Deletion (right to be forgotten)
Two paths:
- Dashboard — Users → search → Delete user.
- API —
POST /v1/apps/:appId/gdpr/deletewith a signed-in operator's WorkOS access token andadminrole.
Deletion:
- Resolves all anonymous aliases linked to the subject.
- Removes the subject graph, consent, responses, engagement, and device tokens.
- Redacts authored request content while preserving unrelated users' engagement.
- Deletes matching analytics data before the job is marked complete.
Submit either an external or anonymous identity:
POST /v1/apps/:appId/gdpr/delete
Authorization: Bearer <workos_access_token>
Content-Type: application/json

{ "externalId": "user_42" }
Access (right of access)
POST /v1/apps/:appId/gdpr/export
Authorization: Bearer <workos_access_token>
Content-Type: application/json

{ "externalId": "user_42" }
The response returns an exportId. Poll
GET /v1/apps/:appId/gdpr/exports/:exportId until the export has completed and
the response includes a short-lived download URL.
Data residency
Processing locations depend on the deployed service and vendor account. The repository does not establish a universal EU-only or Frankfurt-only guarantee. Review the provider inventory and confirm your required locations and transfer safeguards in an executed agreement.
Encryption
- In transit — production configuration requires HTTPS for relevant external services. Certificate pinning is platform- and host-specific, not universal.
- Stored credentials — the backend implements AES-256-GCM with versioned application keys. A per-app cloud-KMS envelope scheme is not established.
- On device — persistence differs by SDK and record. Browser IndexedDB, React Native AsyncStorage, offline queues, and fallback paths must not all be described as encrypted storage. Minimise the data you send.
See Security for the scope and operational verification needs.
DPA & subprocessors
- A DPA review draft and provider inventory are available. Neither establishes an executed customer or vendor agreement.
- Contact [email protected] for current arrangements. The proposed advance notice process needs a verified notification channel before it becomes a contractual commitment.
- Retention and data-rights guidance explain the different scopes of SDK-subject, portal, account, and vendor data.